- Portfolio | Cybersecurity |
Title
Brand Protection: Fake Profile & Scam Website TakedownsDescription
Around one year of brand protection work as a Cyber Security Analyst at Resecurity, Inc. (US). I find and remove impersonation accounts and scam websites targeting large organizations: Facebook pages and profiles, Instagram accounts, WhatsApp numbers, YouTube channels, and fake domains (registrar + hosting abuse reports). Hundreds of takedowns completed. Client names are kept confidential.
Title
Authorized VAPT Engagement - 23 University Web TargetsDescription
As a VAPT intern at the National Cyber Security Academy I took part in an authorized penetration test of 23 web targets for a university, under formal Rules of Engagement. Work included recon, stack fingerprinting, misconfiguration and access-control testing; findings included a High-severity (CVSS 8.6) origin IP exposure that bypassed the Cloudflare WAF, plus HTTP method and security header issues. Reported with CVSS scores and fix steps. Target details are confidential.
Title
Bug Bounty Research on Intigriti (International Programs)Description
Active bug bounty researcher on Intigriti, testing international programs in telecom, e-commerce, publishing, cloud and security-vendor sectors. Methodology: breadth-first asset inventory, then deep manual testing of the highest-value surfaces (access control, IDOR, injection, SSRF, open redirects, WAF bypasses). Every finding is proven with live request/response pairs and written up in platform-format reports.
Title
Vulnerability Disclosure Report - Banking Careers PortalDescription
Responsible-disclosure (VDP) assessment of a banking-sector careers portal built on PeopleSoft HCM. Testing was done through Chrome DevTools because Cloudflare blocked the usual Burp proxy setup. Six findings were documented with evidence and delivered in a professional report with remediation guidance. The organization is not named for confidentiality.
Title
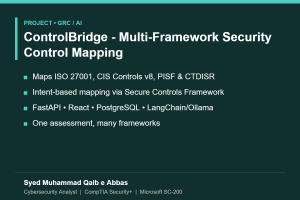
PISF Audit Tool - GRC Risk Assessment PlatformDescription
Final-year project: a control-maturity GRC risk assessment platform built on the Pakistan Information Security Framework (PISF) - 238 controls in 13 domains. Organizations rate each control and the tool computes weighted gaps, an overall risk percentage and Low/Moderate/High/Critical tiers with reports. Stack: React 19, FastAPI, PostgreSQL 16, Caddy, Docker Compose on Oracle Cloud.